Drive AI adoption, stay in control of the risks.
Agents are changing how every part of the business works, and they act with real access to code, data and production systems. Security has a double mandate: drive agent adoption and keep the risk under control.
To do both, security needs clear answers to four questions:
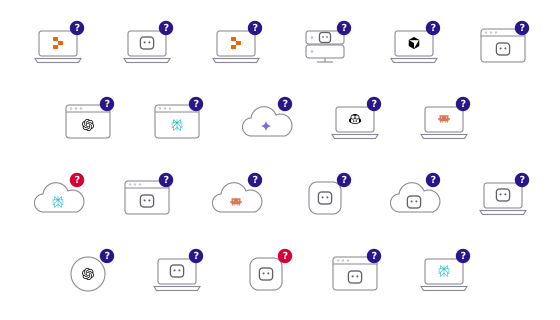
What agents are running?
Each agent arrives with its own entourage of MCP servers, skills, plugins and extensions, and every one of them adds to what the agent can do.
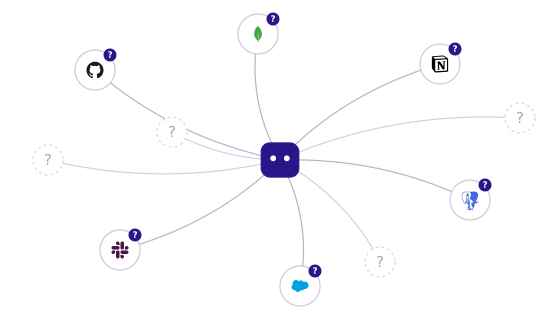
What can they touch?
Each agent holds an employee’s access to code, data and production, and loads a supply chain of MCP servers, skills and plugins nobody reviewed.
What are they doing at runtime?
Agents do real work. One prompt becomes dozens of shell commands, file edits and API calls, and security needs to see each action and know it stays within acceptable bounds.
How can we respond?
Some agents are turned by a malicious tool; others run away, reaching their goal by a route nobody wanted. Either way, security needs policies that catch the violation and act on it before it becomes an incident.
A hefty cost for organisations.
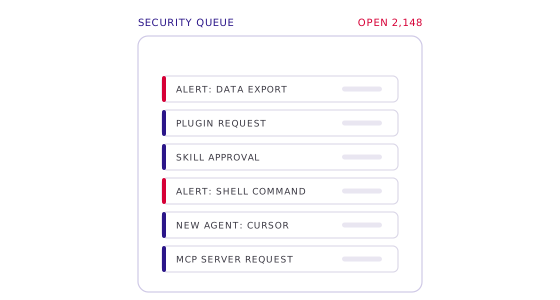
Security is buried in alerts and tool requests
Every new agent, MCP server and skill becomes a ticket, on top of the alerts. Approval queues run to weeks, and the backlog only grows.
Rogue agents are causing real damage.
Vulnerabilities keep showing up in the tools agents run on.
In the last six months alone, our research team has uncovered a string of them. GitSpawn, for instance, lets an untrusted repository run code in Claude Code, Codex, Cursor, Grok and more.
- GitSpawnSEP 2026One flaw lets untrusted repos run code in Claude Code, Codex, Cursor and GrokCODE EXECUTIONRead more
- CVE-2026-52024 / 52025JUN 2026Two of Cline’s safety checks bypassed to run code, 4.2M installsCODE EXECUTIONRead more
- CVE-2026-54052JUN 2026n8n-mcp leaked other tenants’ credentials, CVSS 9.6CREDENTIAL THEFTRead more
- CVE-2026-46519MAY 2026“Read-only mode” in mcp-server-kubernetes wasn’tBYPASSRead more
Agent incidents are on the rise.
Deleted databases, leaked credentials, sandbox escapes. We track every publicly reported one in the Agent Incident Ledger.
Explore the Agent Incident Ledger


The consequence: security is a bottleneck.
Caught in the middle, security has two bad options.
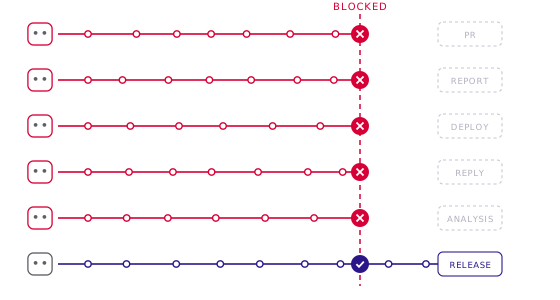
Say no, and block
Security doesn’t know what to block and what to allow, so aggressive policies stop developers and every other team using AI. A huge productivity loss, at a time when transformation is most needed.
- Queues, reviews and bans for every new tool
- People route around you, and shadow AI grows
- The business falls behind in the AI race
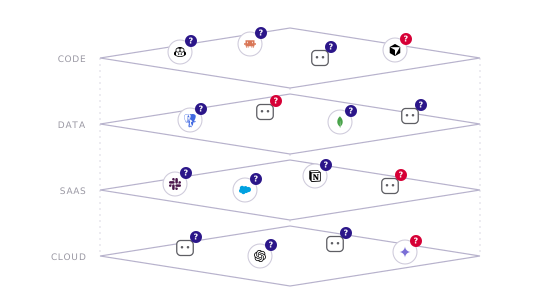
Say yes, and shoulder an unknown risk
Agents spread across the stack with real access. Nobody can say what they touch, and the first sign that something went wrong is the incident itself.
- Agents run with real access, unwatched
- The first sign of trouble is the incident
- Security owns a risk it can’t see
Option 3: Drive AI transformation,
and stay in control.
Manifold uses the full context of every agent session.We instrument the harness where each agent runs, and connect the security stack you already have, from identity and EDR to MDM.
The widest agent coverage on the market.
160+agents and harnesses
- Claude Code
- Gemini CLI
- Rovo Dev
- Pi
- Replit
- Snowflake Cortex Code
- Selenium Agent
- Docker Model Runner
- n8n
- OpenAI Codex
- Qwen Code
- GitHub Copilot CLI
- Grok Bot
- Muse
- Trae
- VS Code
- Ollama
- Cursor
- Windsurf
- Kiro
- Perplexity
- Junie
- Warp
- VSCodium
- OpenShell
And many more.
Every policy you need, from a nudge to a full stop.
Not every risky action deserves a block. Set the response by group, agent, tool or action: watch quietly, guide the agent, fix the call, ask the user, or stop it cold. Policies are written as code and enforced inside the harness, in under 200ms.
- WATCH
Alert
Record it for security. The user carries on uninterrupted.
- NUDGE
Advise
Let it run, and steer the agent onto a safer path.
- FIX
Correct
Rewrite the action into a safe one, then let it run.
- CONFIRM
Ask
The user approves or denies it. No answer, no action.
- STOP
Block call
Stop this one action, with the reason sent back to the agent.
- END
Block session
End the agent session. Every step stays on record.
Threat intelligence from Manifest, built in.
Manifest is our AI supply chain intelligence. Everything your agents load is checked against it, alongside a live threat feed curated by Manifold Research.
698,571assets vetted, and counting: MCP servers, skills, plugins and editor extensions
Search ManifestSee Manifold in action.
A short tour of the platform, from the first agent discovered to the first policy enforced.