See inside every AI agent your workforce runs.
With Manifold, keep every AI agent in sight and under control across endpoints, browsers and the cloud.
- to deploy
- Minutes
- agent types covered
- 100+
- to spot a new agent
- < 1 hour
Your security stack sees only part of what AI agents do.
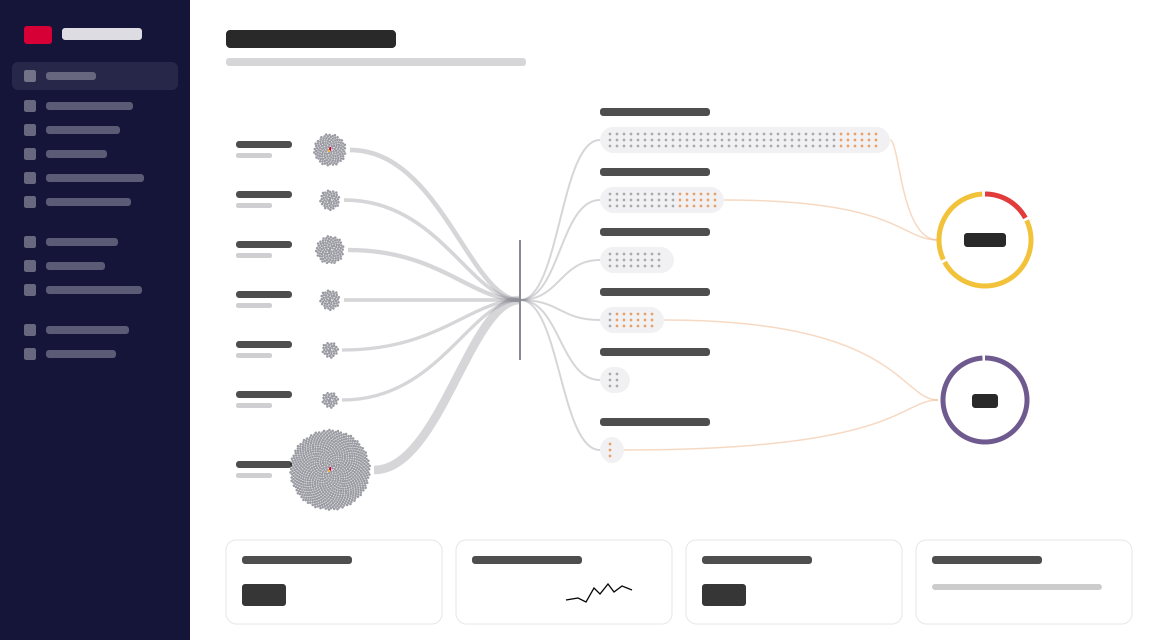
Your employees already run AI agents that use their credentials and permissions. Your tools were built for people and apps, so each one sees a single layer and agents slip between them. Manifold sees inside the agent.
Gateways and proxies
Gateways and proxies see AI traffic at one chokepoint. They miss shadow AI that never routes through them, like the CLI, local MCP servers and personal API keys.
Sees
- Requests routed through the proxy to a model or a remote MCP server
- The traffic at that one boundary
Misses
- Agents nobody pointed at the proxy, like CLIs and shadow AI
- Local MCP servers and the tools built into the agent
- Skills and plugins loaded from disk
- Personal accounts and personal API keys
- Shell commands and file edits
EDR
EDR sees the agent process launch, not what happens inside the session.
Sees
- The agent process starting on the machine
- Activity at the level of the operating system
Misses
- The tool calls and MCP requests the agent makes
- The skills and MCP servers it loaded
- Which person the agent was acting for
Cloud controls
Cloud controls see the workload, not the tools, skills and access the agent itself has.
Sees
- The VM, container or workload the agent runs in
Misses
- The tools, skills and MCP servers the agent loads
- The access and credentials the agent holds
- What the agent does in each session
This lets Manifold find your agents and their supply chain, and step in the moment one turns risky. Routine work runs without a ticket or a block.
Quick to deploy
Rolls out through your existing MDM, with no proxy or network changes.
Covers every surface
Endpoints, browsers, VMs and the cloud, from one platform.
Sees every action
Tool calls, MCP requests, file access and commands at runtime, each linked to the person the agent acted for.
The platform
Discover all agents
One inventory for all your agents, approved or shadow, and their supply chain: MCP servers, skills and extensions.
Explore DiscoverAssess the risk
Assess each agent’s risk and know what to fix first, backed by Manifest research and threat intelligence.
Explore AssessAct at runtime
Pick the response that fits the risk: Alert, Ask, Advise, Correct, Block call or Block session. Most responses keep work moving. Blocking is kept for clear-cut cases.
Explore ActFits the stack you have.
Works with your identity provider, SIEM, ticketing and Slack.
 Okta
 Microsoft Entra ID

 Jira
 Slack
What our customers say
We had ten thousand developers running agents and an MCP approval queue weeks long. Now we govern the actions, not the tickets.
AI agents are hard to control. It is not clear what they do. This is where Manifold comes in. You would think safety means going slower, but actually it means trust, and trust in racing means going even faster.
Manifold uncovered agent risk we didn’t know was there. We can now set policies to match each risk without slowing anyone down.
See Manifold in action.
A short tour of the platform, from the first agent discovered to the first policy enforced.